Data minimization
Collect and move only what the defined purpose requires.
Data, authorized roles, deployment, retention and recovery are defined before the solution is approved.
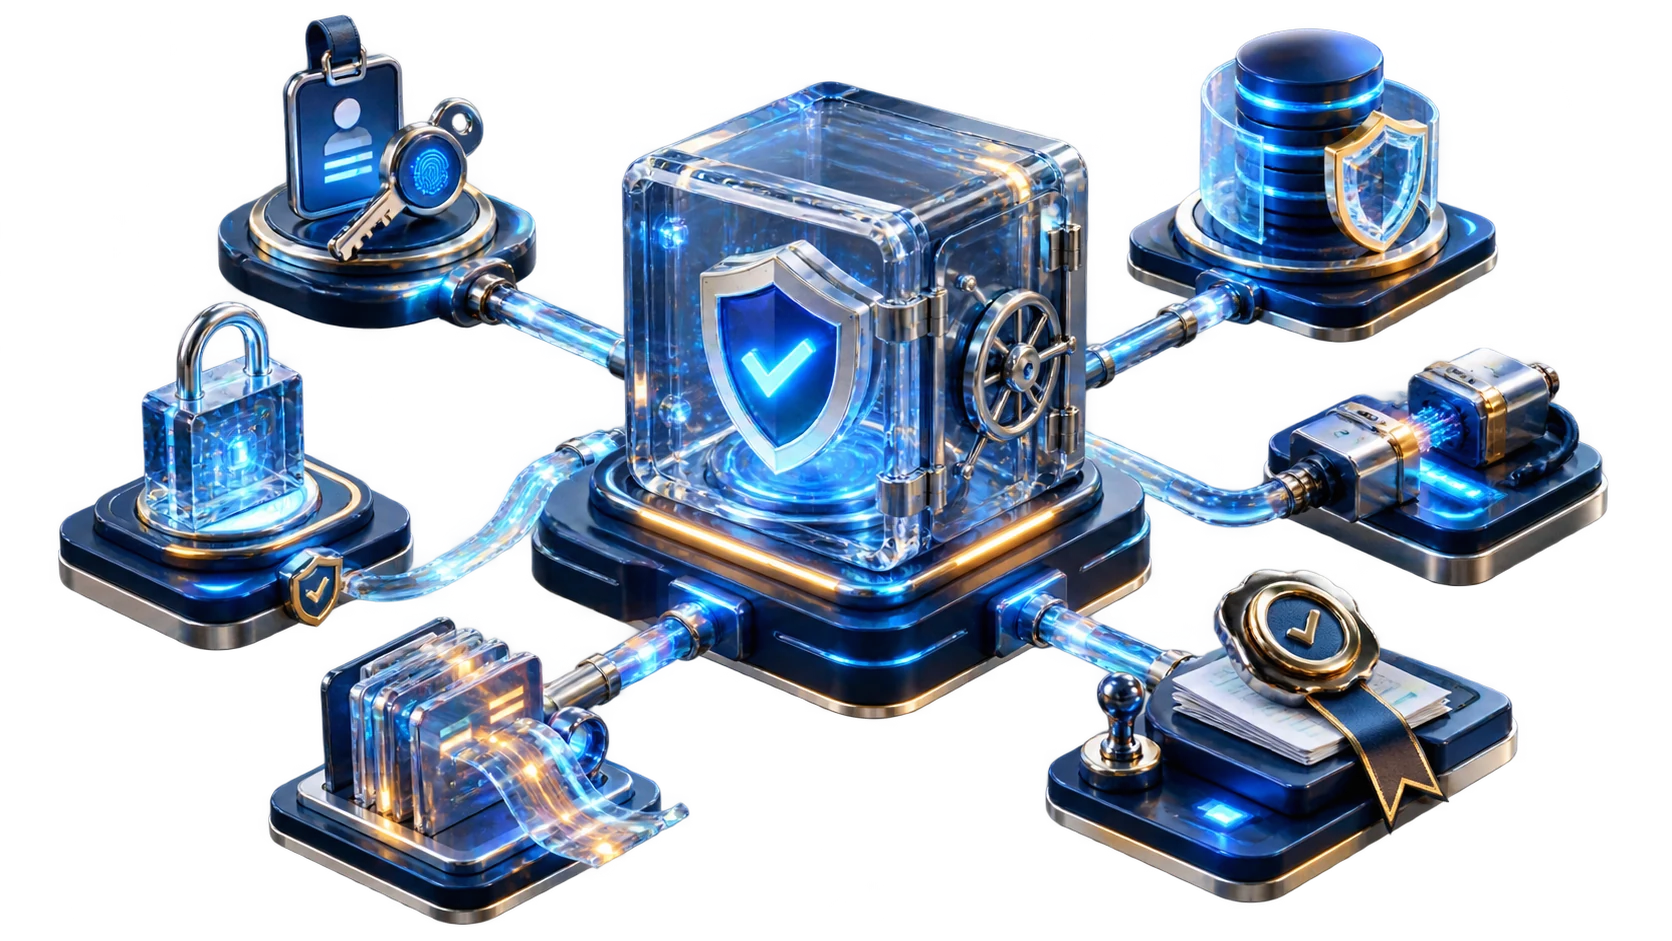
Collect and move only what the defined purpose requires.
Functions and data follow real responsibility.
Cloud, on-premises or hybrid according to product and requirements.
Logs, retention and review are agreed in scope.
Backups are validated through recovery tests.
Outputs, transfer and handover are defined before launch.
Security becomes verifiable when choices, responsibilities and required evidence are written down.
Which environment is intended, and where will data be processed and retained?
Which data is genuinely required for the defined purpose?
Which roles may view, change, export or administer?
What rules apply to data, logs, backups and contract exit?
Which events are logged, who is notified and through which channel?
Which controls, documents and evidence must the entity receive in the proposal?
We review deployment, data, access, retention and integration, then document how each item fits the technical scope.